 Rifan Muazin
 Layla Zulfa
 Nana
 Asro
 Sagoh
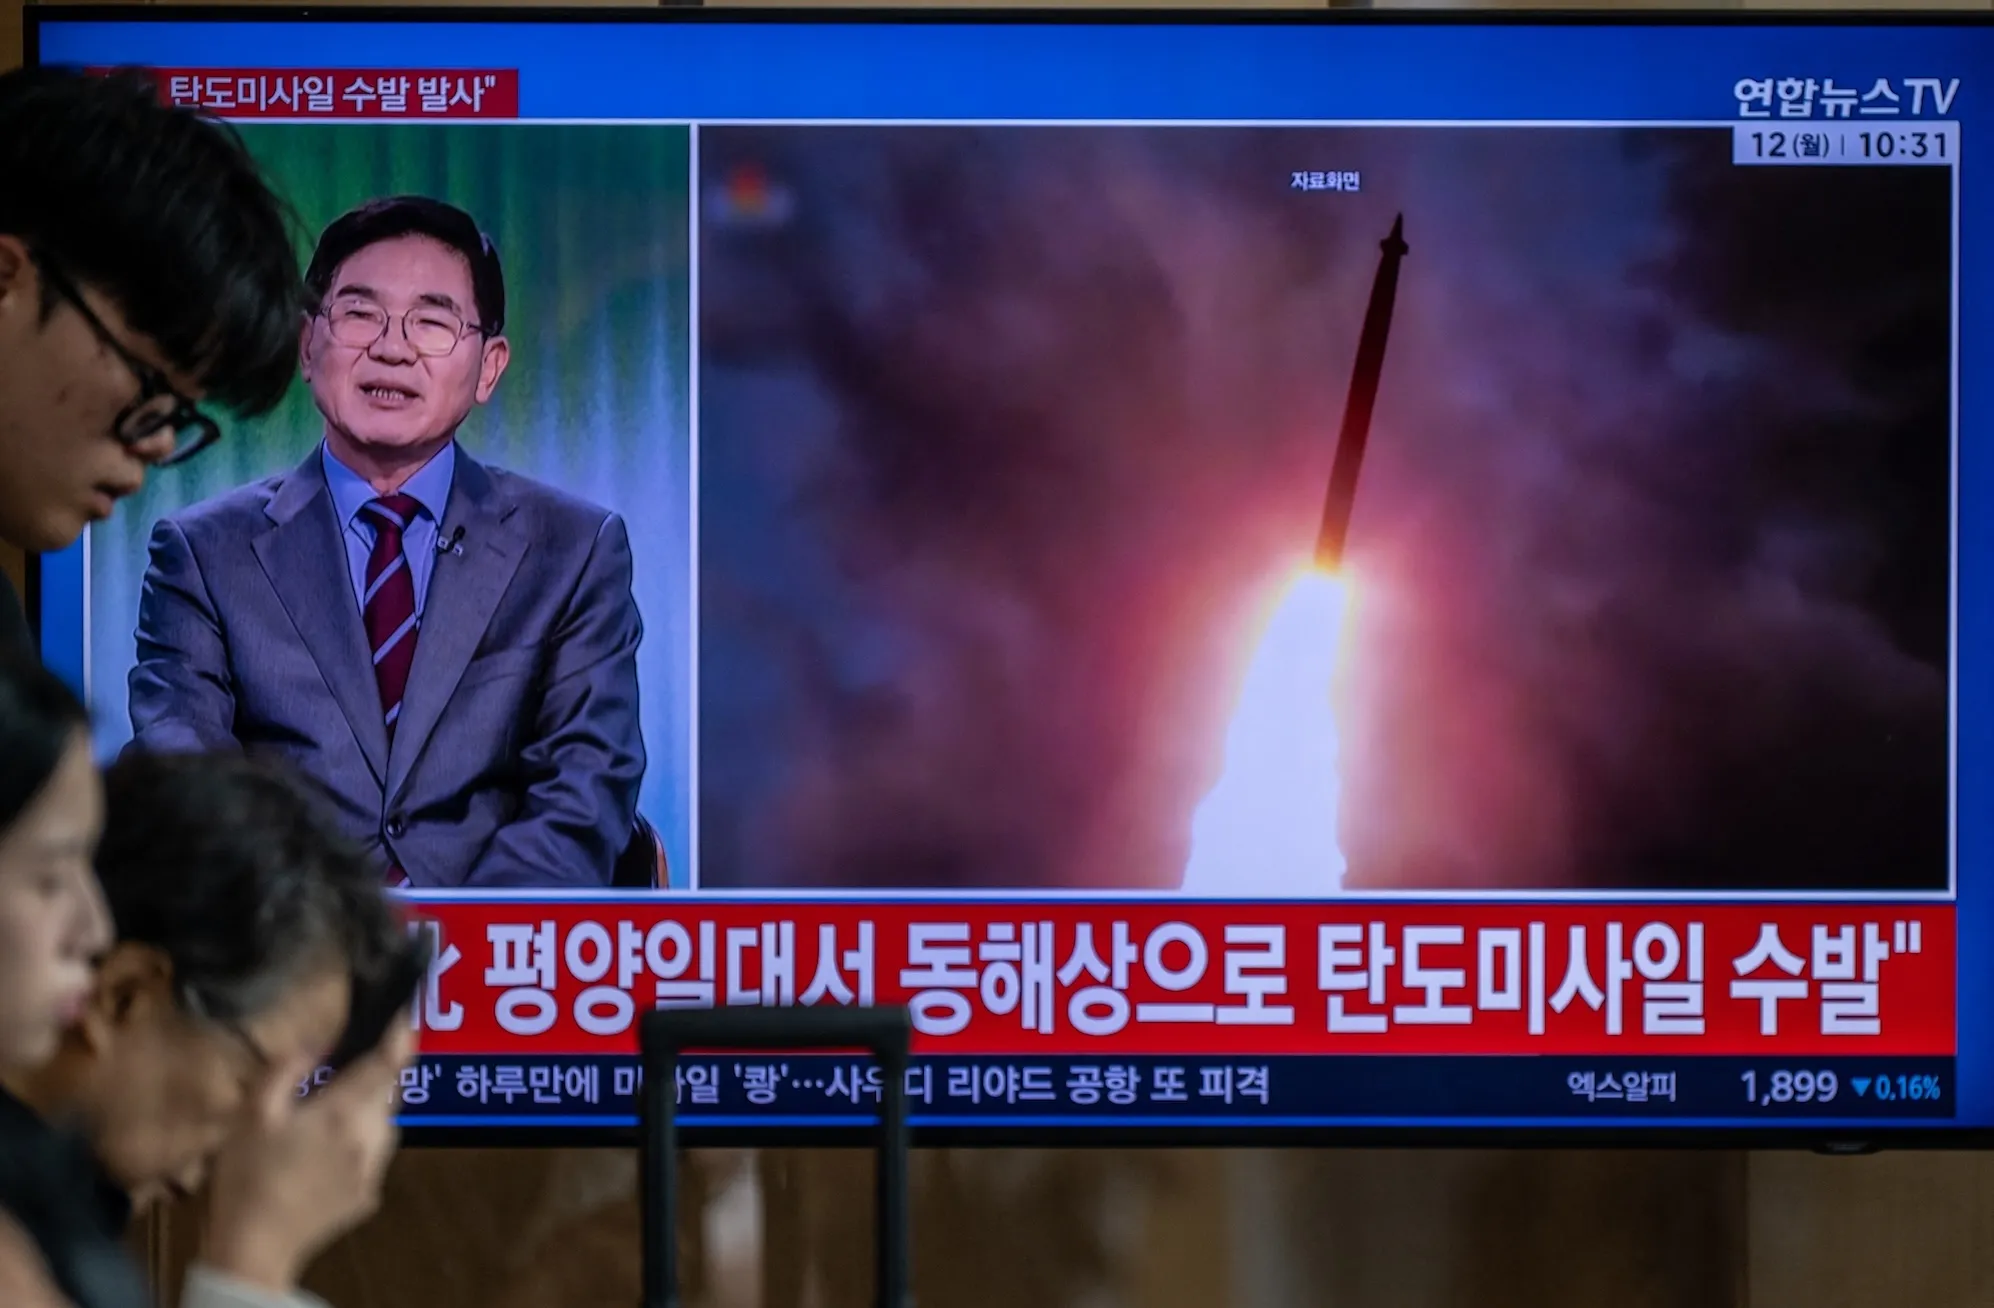
In a chilling revelation that highlights the evolving sophistication of state-sponsored cyber espionage, the U.S. Department of Justice (DOJ) has exposed a vast, clandestine network of “laptop farms” operating within the United States. These hubs, primarily located in residential settings, serve as the physical infrastructure for North Korean intelligence agents who have successfully infiltrated American corporations by posing as remote IT workers.
By leveraging the post-pandemic shift toward remote employment, operatives linked to the Democratic People’s Republic of Korea (DPRK) have successfully bypassed traditional hiring filters, stolen sensitive intellectual property, and siphoned millions of dollars from the U.S. economy. This ongoing operation represents a significant escalation in the regime’s effort to fund its nuclear weapons program through illicit digital means.
The Anatomy of the Laptop Farm Scheme
At the heart of this scheme is a sophisticated blend of identity theft and physical deception. North Korean state-sponsored hackers do not simply attack networks from afar; they infiltrate them from the inside.
According to federal prosecutors, the operation functions through a series of "laptop farms"—residential properties, often in Texas, where rows of company-issued computers are kept powered on and connected to the internet. These computers are assigned to individuals who, on paper, appear to be legitimate, high-skilled U.S. contractors. In reality, these roles are filled by sanctioned North Korean operatives working abroad.
To secure these positions, the hackers utilize stolen identities of American citizens, complete with fabricated social media profiles, sophisticated LinkedIn resumes, and authentic-looking email addresses. Once a company unknowingly hires one of these "workers," they ship a company laptop to a physical address in the U.S.—typically a residence managed by a domestic "facilitator."
These facilitators are American citizens or residents who manage the physical hardware. They keep the machines running, ensure they remain connected to the corporate VPN, and occasionally perform physical tasks required by the company. Meanwhile, the North Korean operative, thousands of miles away, logs into the machine remotely, performs the required coding or IT tasks to maintain the ruse, and simultaneously extracts sensitive data or installs backdoors into the victim’s network.
A Chronology of Infiltration and Enforcement
The recent crackdown, announced Tuesday by the DOJ, marks the culmination of an intensive investigation supported by cybersecurity giant CrowdStrike.
- The Infiltration Phase: Over the last several years, North Korean entities shifted their strategy from traditional external hacking to "insider-as-a-service" models. By exploiting the remote work boom, they successfully embedded operatives into at least 70 U.S.-based companies across 17 states, including Ohio and the District of Columbia.
- The Discovery: Federal authorities identified a pattern of suspicious activity originating from residential IP addresses that were supposedly tied to legitimate employees. Investigations revealed that these addresses were, in fact, the sites of the "laptop farms."
- The Raids: In a coordinated series of enforcement actions, the FBI and DOJ raided over 40 residences across Texas. These searches resulted in the seizure of more than 180 company-issued laptops.
- The Indictments: Prosecutors have officially indicted and arrested at least two individuals identified as domestic facilitators. These individuals provided the "ground game" necessary for the DPRK to bypass the physical, financial, and legal barriers that would otherwise prevent them from operating inside the U.S.
Supporting Data: The Scale of the Threat
The financial and operational scale of this operation is staggering. The DOJ estimates that these North Korean operatives have successfully generated at least $3 million in illicit funds from the infiltrated companies alone. However, experts warn that this figure is likely a conservative estimate that does not account for the long-term cost of intellectual property theft or the extortion campaigns that often follow an initial breach.
The FBI’s Internet Crime Complaint Center (IC3) has issued public warnings suggesting that there are "thousands" of North Korean state-controlled IT workers currently employed at Western firms. These workers do not merely act as spies; they are revenue generators for the regime.
Furthermore, the "laptop farm" scheme is only one pillar of a broader financial strategy. North Korean actors have been linked to:
- Cryptocurrency Theft: In 2025 alone, the regime is estimated to have stolen over $2 billion in cryptocurrency, often targeting exchanges and decentralized finance (DeFi) protocols.
- Open-Source Hijacking: The regime has increasingly targeted open-source developer communities, injecting malicious code into widely used projects to create supply-chain vulnerabilities.
- Hands-on-Keyboard Intrusions: According to CrowdStrike’s threat intelligence reports, North Korean hackers are responsible for approximately 50% of all “hands-on-keyboard” intrusions observed globally over the past year. Unlike automated malware, these human-led attacks allow for precise navigation of corporate networks to locate the most valuable proprietary data.
Official Responses and Strategic Implications
The Department of Justice has been clear in its assessment: the North Korean regime is evolving its tactics to counter private sector detection. "Increasingly, North Korean IT workers are turning to recruiting American facilitators to counter improved private sector detections and law enforcement actions," the DOJ noted in its public announcement.
The strategy has become modular. In many cases, these workers are now subcontracting entire projects to third-party foreign nationals, further obfuscating the trail of responsibility and making it difficult for HR departments to verify the identities of their remote contractors.
The National Security Dimension
The primary motivation for these efforts is the funding of North Korea’s sanctioned nuclear weapons and ballistic missile programs. By utilizing the U.S. labor market as a revenue stream, the regime is effectively turning American corporate payrolls into a source of funding for its military proliferation.
"These workers pose a significant national security and intellectual property theft insider threat," the FBI stated. The implications for companies are severe. Once an operative gains access to a corporate network, they can move laterally, exfiltrate trade secrets, and plant ransomware to extort the company for additional payments.
Looking Forward: How Companies Can Protect Themselves
The DOJ’s latest actions serve as a stark warning to HR departments and IT security teams. The reliance on remote-first hiring, while efficient, has introduced a new vector for state-sponsored espionage.
Security experts recommend several defensive measures to mitigate the risk of "laptop farm" infiltration:
- Strict Identity Verification: Implementing rigorous background checks that include video-based identity verification, rather than relying solely on document uploads.
- Hardware Controls: Ensuring that company-issued hardware is equipped with persistent monitoring and geo-fencing capabilities that flag access from unauthorized locations.
- Network Behavior Analytics: Utilizing advanced endpoint detection and response (EDR) tools to identify "hands-on-keyboard" behavior that deviates from standard employee patterns.
- Vetting Contractors: Treating remote, contract-based IT workers with the same level of security scrutiny as full-time, in-house employees, particularly regarding network access privileges.
As the international community continues to sanction the DPRK, the regime’s reliance on these illicit, creative, and highly effective methods of revenue generation is expected to grow. The "laptop farm" busts in Texas are a significant victory for law enforcement, but they also serve as a grim indicator that the front lines of global geopolitics have shifted from the DMZ to the remote home offices of American employees.
For the U.S. corporate sector, the message is clear: the digital workforce is no longer just a matter of convenience; it is a critical front in the ongoing battle against state-sponsored cyber warfare. Vigilance, scrutiny, and a shift toward "zero-trust" employment models may be the only way to prevent the next wave of silent, high-stakes intrusions.

 Siti Muinah